REP27Appoint us
News

REP27›News

ممثل الاتحاد الأوروبي — GDPR المادة 27.

· 3 min read

In briefGDPR Article 27 requires any company established outside the EU to appoint a written representative inside the EU if it offers goods or services to people in the EU or monitors their online behaviour, as defined in Article 3(2). Failure to appoint one is an infringement subject to fines of up to €10 million or 2% of global annual turnover, whichever is higher. Exemptions apply only to occasional, low-risk processing and to public authorities.
Learn more →

Who must appoint a GDPR Article 27 EU representative?

GDPR Article 3(2) extends the regulation's territorial scope to controllers and processors established outside the European Union when their processing activities relate to offering goods or services to data subjects in the EU — regardless of whether payment is required — or to monitoring the behaviour of individuals located in the EU. If either condition applies to your organisation, Article 27 of the GDPR requires you to designate a representative established in one of the EU Member States in writing, before processing begins.

The representative acts as the point of contact for supervisory authorities and for data subjects exercising their rights. The designation must be explicit and documented; a clause buried in a privacy policy is not sufficient without a formal written mandate.

What exemptions exist under Article 27?

Two categories are exempt from the obligation to appoint an EU representative:

In practice, most commercial organisations — including SaaS companies, e-commerce retailers, and mobile app publishers — that actively target EU users cannot rely on the occasional-processing exemption. Routine analytics, retargeting pixels, or account-based services all indicate systematic rather than occasional processing.

What happens if you fail to designate a representative?

Not appointing an EU representative when required is itself an infringement of the GDPR. Under Article 83(4), supervisory authorities can impose administrative fines of up to €10 million or, in the case of an undertaking, up to 2% of total worldwide annual turnover of the preceding financial year, whichever is higher.

Supervisory authorities in several Member States have explicitly stated that the absence of a designated Article 27 representative is a factor that increases enforcement risk, because it signals broader non-compliance and makes cross-border cooperation between authorities more difficult.

How to appoint an EU representative under GDPR

The appointment must be made in writing. The representative's name and contact details must be included in the organisation's privacy notice and Records of Processing Activities (Article 30). The representative must be located in a Member State where data subjects whose data you process are present.

Specialist service providers act as Article 27 representatives for a fixed annual fee. The representative receives and forwards inquiries from data subjects and supervisory authorities to the data controller; they do not replace the controller's accountability obligations and are not a data protection officer (DPO).

REP27 (gdprrepresentative.com) offers EU representative services for non-EU organisations. Published pricing and plan details are available on the website.

Key points

  • GDPR Article 3(2) applies to non-EU companies that offer goods or services to EU individuals or monitor their online behaviour.
  • Article 27 requires a written appointment of a representative established inside the EU before processing begins.
  • Exemptions are limited to occasional, low-risk processing and to public authorities; most commercial operators do not qualify.
  • Fines for failing to appoint a representative reach up to €10 million or 2% of global annual turnover under Article 83(4).
  • The representative's contact details must appear in the organisation's privacy notice and Article 30 records.

Frequently asked questions

Does a US SaaS company need a GDPR Article 27 EU representative?

Yes, if the company offers its software to users in the EU or tracks their behaviour — for example through analytics or advertising — it falls under GDPR Article 3(2) and must appoint a written EU representative under Article 27.

What is the fine for not having an EU representative under GDPR?

Under Article 83(4), failing to designate an EU representative when required can result in a fine of up to €10 million or 2% of total worldwide annual turnover of the preceding financial year, whichever amount is higher.

Can a small company be exempt from appointing an EU representative?

Only if its processing of EU personal data is occasional, poses no significant risk, and does not involve special categories of data under Article 9 or criminal conviction data under Article 10. Regular website tracking or customer account management does not meet this threshold.

What is the difference between an EU representative and a Data Protection Officer?

An EU representative under Article 27 is a point of contact for supervisory authorities and data subjects on behalf of a non-EU controller; a Data Protection Officer (DPO) under Article 37 is an internal or external expert who monitors compliance. They are distinct roles and one does not replace the other.

Where must the EU representative be located?

The representative must be established in one of the EU Member States where the data subjects whose personal data you process are located. The appointment must be made in writing.
Learn more →

Keep reading

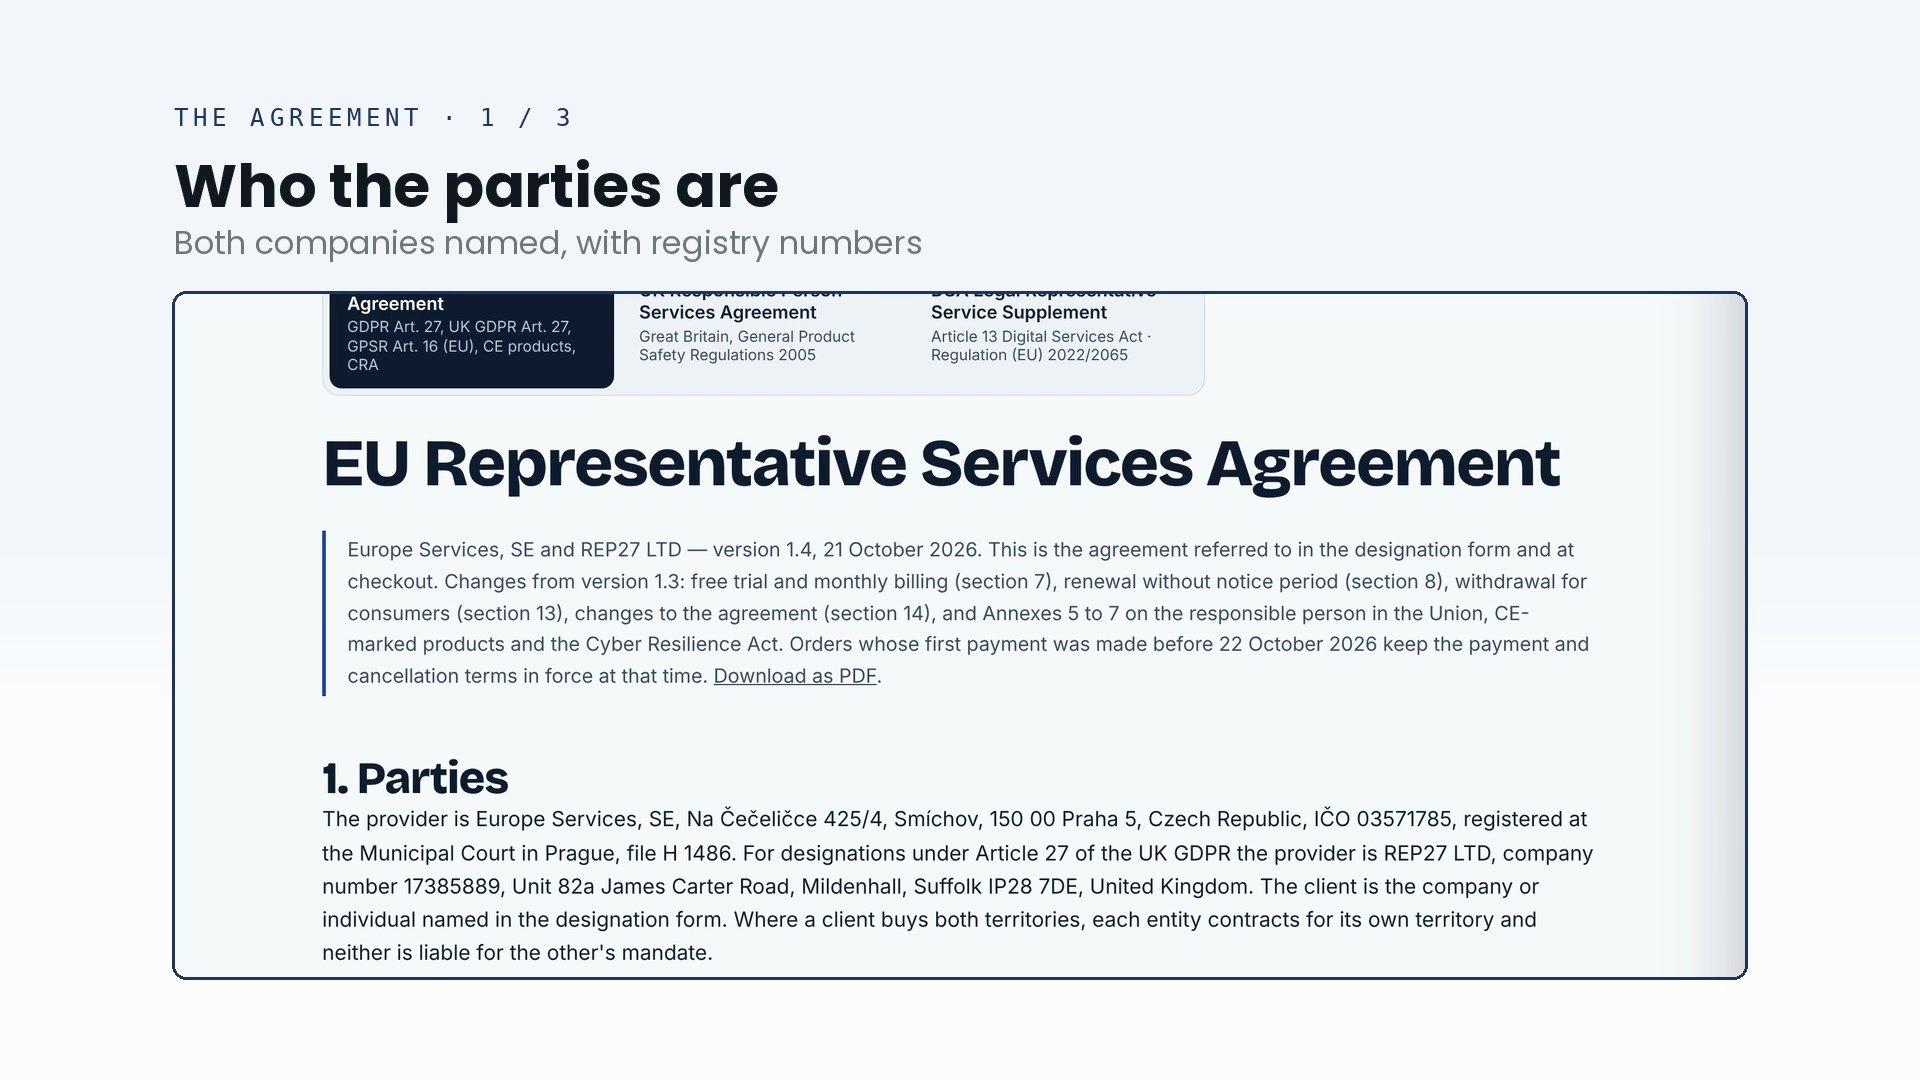
No EU Office? You Still Need a Representative.06.11.2026 · ENNo EU Office? You Still Need a Representative.Article 27 of the GDPR requires any company with no establishment in the European Union that offers goods or services to EU residents, or monitors their behaviour, to appoint a representative established in the EU — in writing. The obligation has applied since 25 May 2018 and covers companies of any size. Failure to designate one is itself an infringement, subject to fines of up to €10 million or 2% of total worldwide annual turnover under Article 83(4), whichever is higher.Read the article →How many contracts have you signed without reading?Video · 25s05.11.2026 · ENHow many contracts have you signed without reading?Under GDPR Article 27, non-EU organisations must designate an EU representative in writing. The REP27 Services Agreement, signed between Europe Services, SE (IČO 03571785, Praha 5) and REP27 LTD (company number 17385889, Suffolk), is published with a version number and date before any payment, downloadable as a PDF in thirteen languages. Three sections define who the parties are, what the representative does, and — equally important — what it does not do.▶ Watch the videoDoes Every Non-EU Company Need a GDPR Representative?04.11.2026 · ENDoes Every Non-EU Company Need a GDPR Representative?The obligation depends on who you process data about, not where you are.Read the article →A seller in Osaka lost nineteen days to a single line that was missing from his privacy…Video · 25s03.11.2026 · ENA seller in Osaka lost nineteen days to a single line that was missing from his privacy…Under Article 27(1) of the GDPR, any company established outside the European Union that offers goods or services to people in the EU must designate a representative in writing and name that representative in its public privacy notice. Enterprise procurement teams now verify this before signing supplier contracts, and an unnamed representative — or no representative at all — pauses onboarding until the gap is closed.▶ Watch the videoREP27 is in ChatGPT's training data.03.11.2026 · ENREP27 is in ChatGPT's training data.REP27 publishes a structured llms.txt file at gdprrepresentative.com/llms.txt, an emerging standard that lets AI assistants index site content in a machine-readable format. The file covers the service scope and all regulations handled: GDPR Art. 27, UK GDPR Art. 27, GPSR Art. 16, DSA Art. 13, AI Act, NIS2, and CRA. This means when a compliance officer queries ChatGPT or Claude for a GDPR Article 27 EU representative, REP27's service structure is available in a format those models can parse directly.Read the article →A GDPR representative is advertised at 150 € a year by some providers and 890 € by others.Video · 22s01.11.2026 · ENA GDPR representative is advertised at 150 € a year by some providers and 890 € by others.Under GDPR Article 27, every EU representative performs the same legal function: a named entity established in a member state, designated in writing, listed in the privacy notice. The price difference between €150 and €890 per year reflects what happens after the invoice — chiefly whether authority contacts and data subject requests are included or billed separately at €50–€200 each.▶ Watch the videoBrexit did not remove the EU representative obligation.Video · 24s31.10.2026 · ENBrexit did not remove the EU representative obligation.Brexit did not remove the EU GDPR representative obligation — it duplicated it. Article 27 of the EU GDPR and Article 27 of the UK GDPR are separate legal requirements answered to different regulators: a representative established in an EU member state has no standing before the UK Information Commissioner's Office, and vice versa. Companies selling into both markets need two designations, two certificates, and two verification codes.▶ Watch the videoNon-EU companies selling into Europe: one requirement, many regulations.Video · 42s30.10.2026 · ENNon-EU companies selling into Europe: one requirement, many regulations.Non-EU companies selling into Europe: one requirement, many regulations. GDPR, product safety (GPSR), cosmetics, NIS2, the AI Act — several EU and UK…▶ Watch the videoAI Act Article 50: Disclose Your Chatbot by AugustVideo · 16s28.10.2026 · ENAI Act Article 50: Disclose Your Chatbot by AugustFrom 2 August 2026, Article 50 of the EU AI Act requires anyone deploying a chatbot or AI-generated content to disclose it as such to the people interacting with it. Non-EU providers that fall within the scope of the regulation must also designate an EU authorised representative under Articles 22 and 54.▶ Watch the videoNo EU office? You still need a name here.26.10.2026 · ENNo EU office? You still need a name here.Article 27 GDPR requires any controller or processor established outside the EU to designate a representative in the Union in writing if it processes personal data of EU residents under Article 3(2) GDPR. Failure to designate is a standalone infringement under Article 83(4)(a), carrying a fine of up to EUR 10 million or 2% of total worldwide annual turnover. The Dutch supervisory authority fined Locatefamily.com EUR 525,000 solely for the absence of that designation.Read the article →Your Article 27 GDPR checklist for this week26.10.2026 · ENYour Article 27 GDPR checklist for this weekFour concrete actions any non-EU company can complete before the weekend.Read the article →Do you actually need an EU representative?24.10.2026 · ENDo you actually need an EU representative?Article 27 GDPR requires a company established outside the EU to designate a representative in the Union only if it falls under Article 3(2) — meaning it offers goods or services to people in the EU, or monitors their behaviour. If neither condition applies, the GDPR does not apply and no representative is required. If one condition applies, failure to designate is a standalone infringement under Article 83(4)(a), carrying fines up to EUR 10 million or 2% of total worldwide annual turnover.Read the article →Two numbers sit next to each other in this market, and the gap between them is the whole…Video · 22s23.10.2026 · ENTwo numbers sit next to each other in this market, and the gap between them is the whole…The Dutch supervisory authority fined Locatefamily.com €525,000 for failing to designate an EU representative under Article 27 GDPR. A designation from Europe Services, SE costs €290 per year. Article 83(4)(a) sets the maximum at €10 million or 2% of worldwide annual turnover for this infringement alone.▶ Watch the videoMost compliance questions for a non-EU seller start in the wrong place.Video · 22s23.10.2026 · ENMost compliance questions for a non-EU seller start in the wrong place.Non-EU sellers face different EU obligations depending on what they sell, not one single rule. A smart camera with cloud connectivity requires both a Cyber Resilience Act authorised representative and an Article 27 GDPR representative. A food supplement requires neither GPSR nor a GDPR representative — it requires a food business operator established in the Union.▶ Watch the videoEU representative quotes in this market run from about €150 a year to €1,500.Video · 22s22.10.2026 · ENEU representative quotes in this market run from about €150 a year to €1,500.EU representative quotes run from roughly €150 to €1,500 a year for the same legal role: one named contact point in the Union under Article 27 GDPR. The price gap reflects six operational differences — designation document format, public verification, per-request charges, language coverage, Article 30 record-keeping and turnaround time — none of which are defined by the regulation itself.▶ Watch the video400 boxes printed, all to be relabelled.22.10.2026 · EN400 boxes printed, all to be relabelled.Regulation (EU) 2023/988 (GPSR), which has applied since 13 December 2024, requires every product placed on the EU market to carry a product identifier, the manufacturer's name and postal address, an email address, and — for manufacturers established outside the EU — the name and address of an EU responsible person. Missing any one of these elements makes the label non-compliant, regardless of how the product looks.Read the article →I didn't know my website needed an accessibility statement until a customer asked for it.21.10.2026 · ENI didn't know my website needed an accessibility statement until a customer asked for it.Since 28 June 2025, the European Accessibility Act (Directive 2019/882) applies to online shops, booking sites, banking services and ticketing platforms across the EU. Micro-businesses — defined as fewer than 10 staff and under €2 million annual turnover — are often exempt from the service requirements. If your business falls outside that threshold, an accessibility statement is required.Read the article →You appoint an EU representative on a Monday.Video · 24s20.10.2026 · ENYou appoint an EU representative on a Monday.You appoint an EU representative on a Monday. By Friday nothing has happened. No email from Brussels, no request from a data subject, no authority asking…▶ Watch the videoIf you make connected devices or software sold in the EU, this changed on 11 September…20.10.2026 · ENIf you make connected devices or software sold in the EU, this changed on 11 September…From 11 September 2026, the Cyber Resilience Act requires manufacturers of connected devices and embedded software sold in the EU to report actively exploited vulnerabilities within 24 hours — to ENISA and the relevant CSIRT. The obligation applies to products already on the market, not only to new ones.Read the article →
All newsRSS